> For the complete documentation index, see [llms.txt](https://enterprise.hideez.com/llms.txt). Markdown versions of documentation pages are available by appending `.md` to page URLs; this page is available as [Markdown](https://enterprise.hideez.com/hideez-server-integration/saml-integration/okta.md).

# Okta

## **Setting Up Okta**

**1. Sign in to Okta Admin Console**

Log in to your **Okta Admin Console**.

<figure><img src="https://1669663611-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FRdTysrljwe610dPFG7tE%2Fuploads%2FSuZmeMuZfvQSGiHagrTp%2Fimage.png?alt=media&amp;token=a1e80446-eb4e-4c04-9b8b-a0eccf6b5377" alt="" width="563"><figcaption></figcaption></figure>

**2. Navigate to Identity Providers**

In the left navigation panel, go to **Security → Identity Providers**.

**3. Add an Identity Provider**

* Open the **Identity Providers** tab.
* Click **Add Identity Provider**.

<figure><img src="https://1669663611-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FRdTysrljwe610dPFG7tE%2Fuploads%2FPAWOp6buHGiLgdBmpaCr%2Fimage.png?alt=media&amp;token=b45c006a-edd3-4841-a6d9-f62259aaf02e" alt="" width="563"><figcaption></figcaption></figure>

* Ensure that the **Select an Identity Provider** list includes **"SAML 2.0 IdP"**.

<figure><img src="https://1669663611-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FRdTysrljwe610dPFG7tE%2Fuploads%2FDyqhAy8knd8Xg2enQ2GA%2Fimage.png?alt=media&amp;token=2b9fdb4a-516c-475e-86f7-42d4ef7594ba" alt="" width="563"><figcaption></figcaption></figure>

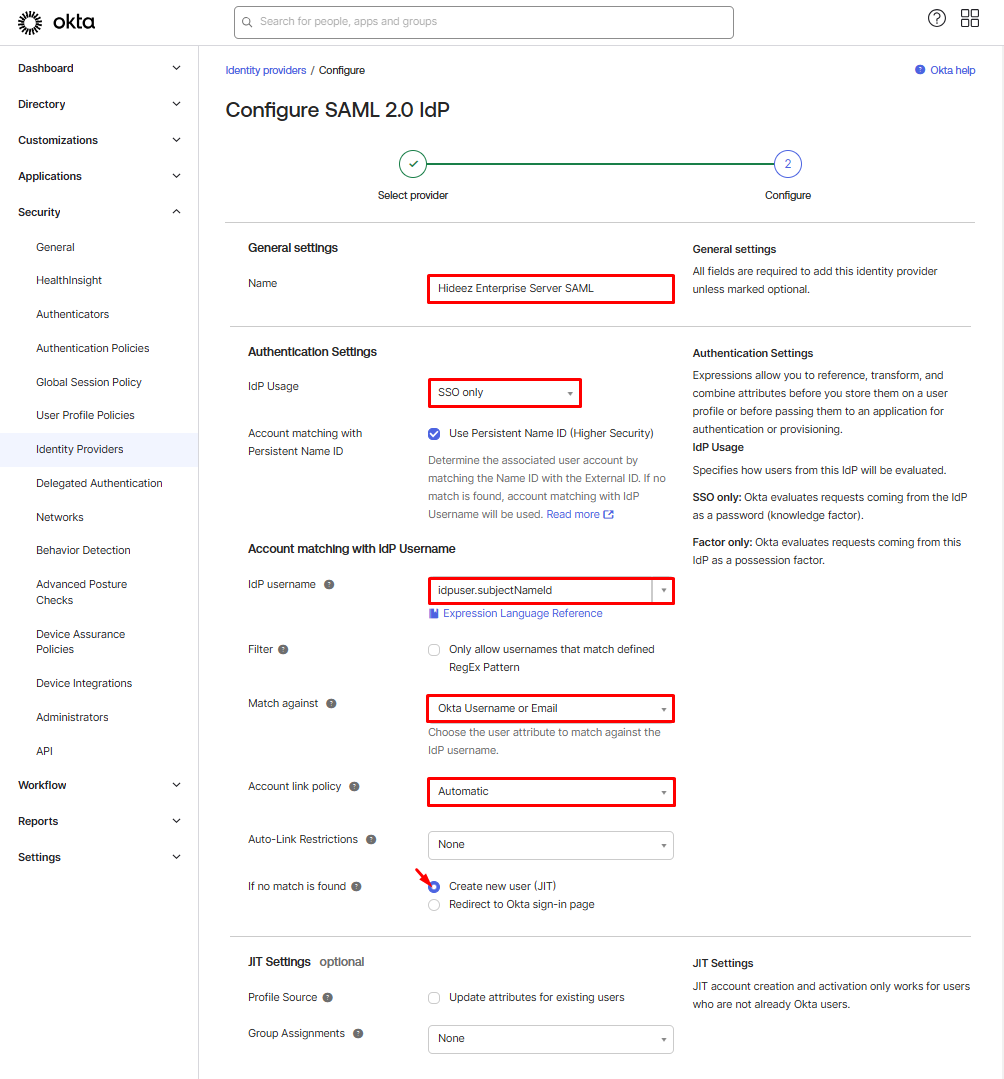
**4. Configure SAML 2.0 IdP**

Set up the required parameters for **SAML 2.0 IdP**.

<figure><img src="https://1669663611-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FRdTysrljwe610dPFG7tE%2Fuploads%2FDQhBYurQxzbZNv5xsX55%2Fimage.png?alt=media&amp;token=19936862-d9f7-4656-b519-9523e0c3bb34" alt="" width="563"><figcaption></figcaption></figure>

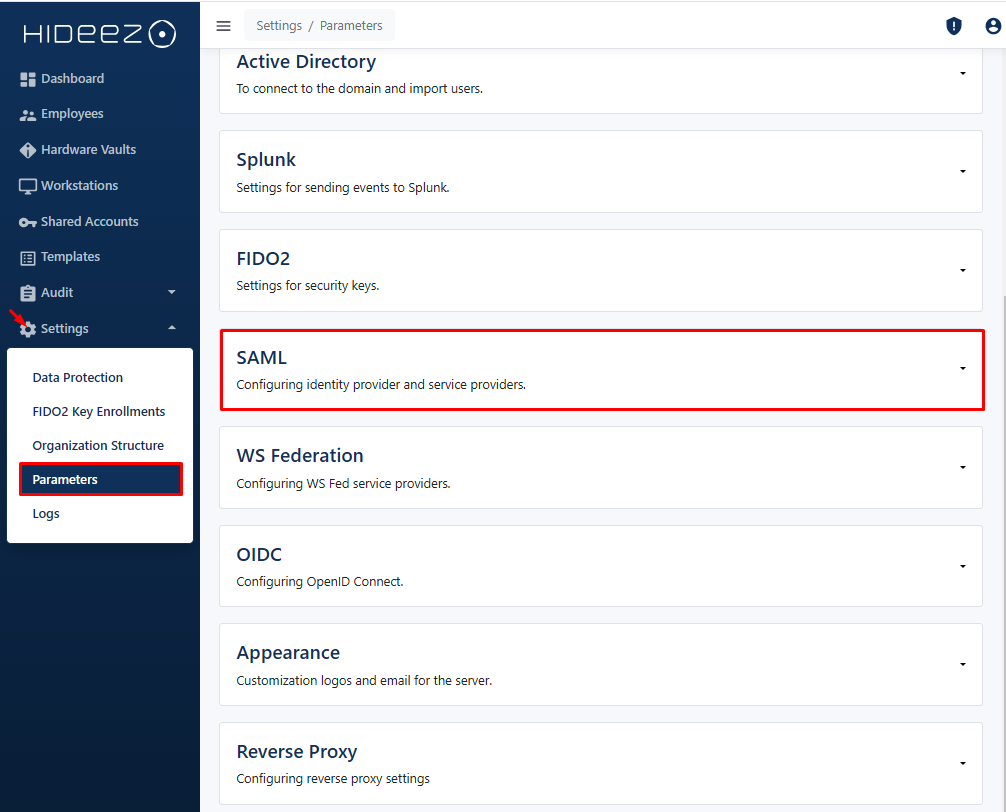
**5. Sign in to Hideez Enterprise Server and navigate to Settings→Parameter**s

<figure><img src="https://1669663611-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FRdTysrljwe610dPFG7tE%2Fuploads%2FvjZ0qS4OjvvtV6SkerqH%2Fimage.png?alt=media&amp;token=fc43e274-67a9-4162-ac19-4a35892345d8" alt="" width="563"><figcaption></figcaption></figure>

**8. Enter the necessary Identity  Provider (IdP) configuration details.**&#x20;

<figure><img src="https://1669663611-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FRdTysrljwe610dPFG7tE%2Fuploads%2FGsSbzVf3zGtq2eCFYBNz%2Fimage.png?alt=media&amp;token=31a02851-f6e9-4906-9bc7-e833aa13fbc6" alt=""><figcaption></figcaption></figure>

**7. Create a New SAML Integration**

* Click the **Add Service Provider** button.

<figure><img src="https://1669663611-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FRdTysrljwe610dPFG7tE%2Fuploads%2F4FNq9RDQemHOAAHV3W0m%2Fimage.png?alt=media&amp;token=58c03f19-8ad0-45bb-8a2c-de8c53f347c8" alt="" width="563"><figcaption></figcaption></figure>

**8. Enter the required Service Provider (SP) configuration details:**

<figure><img src="https://1669663611-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FRdTysrljwe610dPFG7tE%2Fuploads%2Fhy51PrpnwovrsDkDIXar%2Fimage.png?alt=media&amp;token=6daa1772-692f-4bbd-88a0-73eb022a10d4" alt=""><figcaption></figcaption></figure>

* **Name**: Okta
* **Issuer / SP Entity ID**: `https://www.okta.com/saml2/service-provider/+id from Okta`
* **Assertion Consumer Service (ACS) URL**: Your OKTA tenant’s address (e.g., `https://dev-48458662.okta.com/sso/saml2/+id from Okta`)
* Click **Add**.

## **Set Up Routing Rules**

**1. Navigate to Routing Rules**

* Go to the **Routing Rules** tab.
* Click **Add Rule**.

<figure><img src="https://1669663611-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FRdTysrljwe610dPFG7tE%2Fuploads%2FZu0wNmUDhNvJ76dD0Eq2%2Fimage.png?alt=media&amp;token=a58ee49e-97cb-4a65-ae8b-bdde47aa17e1" alt="" width="563"><figcaption></figcaption></figure>

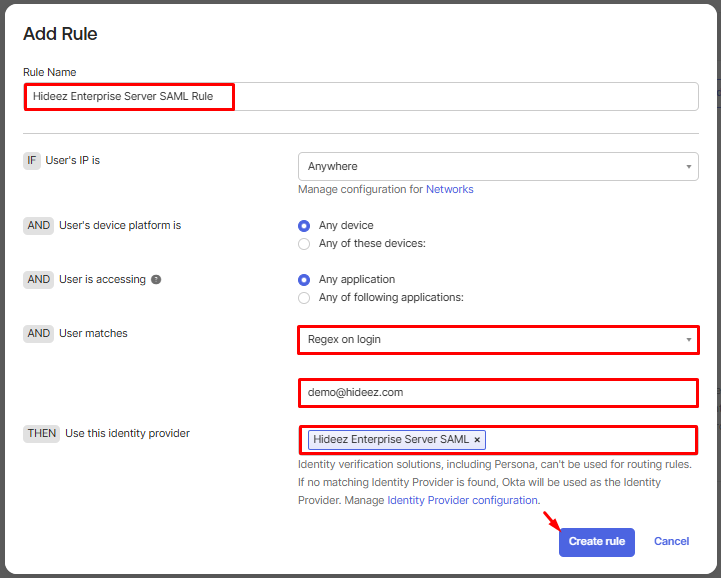
**2. Define the Rule Conditions**

* Configure the required conditions for authentication.

<figure><img src="https://1669663611-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FRdTysrljwe610dPFG7tE%2Fuploads%2FV0vuadwEhuT7pKVxVytg%2Fimage.png?alt=media&amp;token=e15d2bef-5a90-4af5-8dc5-3002b469ecbe" alt="" width="541"><figcaption></figcaption></figure>

* Click **Create Rule**.
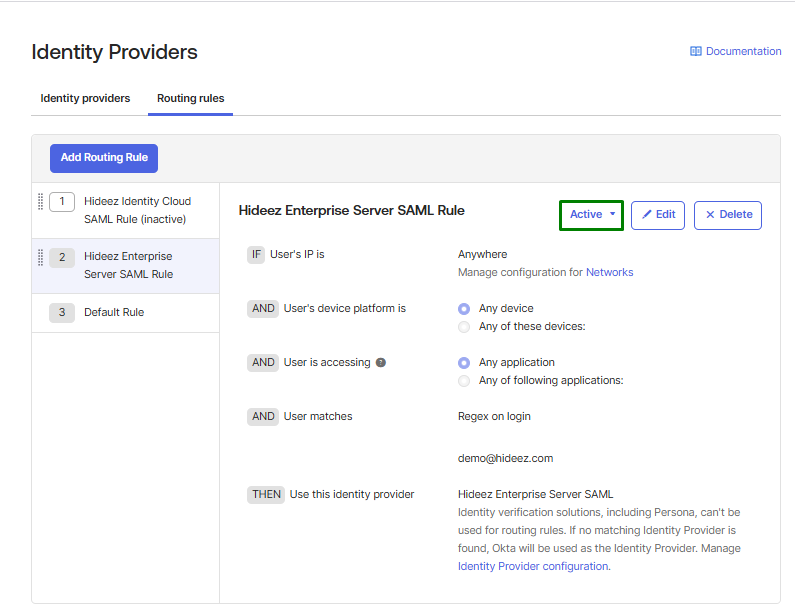
* Activate the rule.

<div><figure><img src="https://1669663611-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FRdTysrljwe610dPFG7tE%2Fuploads%2FIXNjl6riN2kOvdQuIOPn%2Fimage.png?alt=media&amp;token=ed2b854c-dcb3-4f37-a58b-19c1c5da3f35" alt=""><figcaption></figcaption></figure> <figure><img src="https://1669663611-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FRdTysrljwe610dPFG7tE%2Fuploads%2FeQiZapOUicZOc01TiELm%2Fimage.png?alt=media&amp;token=6fcace5c-bc21-4304-bf0e-d7f90fe73fe4" alt=""><figcaption></figcaption></figure></div>

{% hint style="info" %}

#### **Notice**

Next time you sign in to **Okta**, you will be automatically redirected to **Hideez Enterprise Server** as the **Identity Provider (IdP)**. After successfully signing in to **Hideez Enterprise Server**, you will be redirected back to **Okta**, completing the authentication process.
{% endhint %}